General
Concepts, terminology and models (62443-1).
IEC 62443 · Industrial cybersecurity
Protect your plants, OT networks and automation systems with the international standard adopted by operators, integrators and manufacturers.
What is IEC 62443?
ISA/IEC 62443 is a series of standards that defines how to protect industrial automation and control systems (IACS): PLCs, SCADA, DCS, sensors and the networks that connect them.
Unlike ISO 27001, it puts availability and process safety first: the plant has to keep running even under attack.
It assigns responsibilities to every player in the ecosystem: the asset owner, the system integrator and the component manufacturer.
Structure of the series
Concepts, terminology and models (62443-1).
Security program for the asset owner and service providers (62443-2).
Risk assessment, zones and conduits, and technical requirements per security level (62443-3).
Secure product development and technical requirements for each component (62443-4).
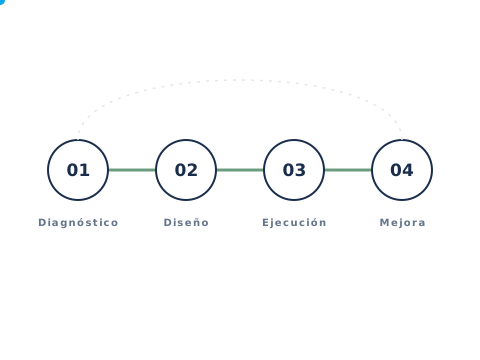
Phases
Security levels
Protection against accidental errors or violations.
Against intentional attacks with simple means and few resources.
Against sophisticated attacks with moderate resources and knowledge of the industrial environment.
Against sophisticated attacks with extensive resources, such as state-sponsored ones.
Why IEC 62443
You reduce the risk of ransomware halting production.
You segment without disrupting operations or plant schedules.
A technical foundation for NIS2 and critical infrastructure requirements.
Certified manufacturers and integrators win industrial tenders.
Who it applies to
FAQ
It is the international series of cybersecurity standards for industrial automation and control systems. It sets requirements for asset owners, integrators and manufacturers, with security levels based on the threat.
ISO 27001 manages information security across the whole organization. IEC 62443 focuses on industrial control systems, where availability and process safety come first. They complement each other.
Yes. Accredited bodies certify the security programs of asset owners and integrators, system security, and manufacturers’ processes and products.
No. We survey with passive techniques and schedule changes within maintenance windows so operations are not affected.
We assess your OT network and build an IEC 62443 plan without stopping production.