Governance
Management approves the measures, oversees their implementation and is accountable for them.
NIS2 · Directive (EU) 2022/2555
We determine whether it applies to you, measure your gap and help you meet the risk management and incident reporting obligations.
What is NIS2?
NIS2 replaces the 2016 NIS directive: it expands the scope to 18 sectors, tightens obligations and raises penalties.
Each Member State adopts it through its own law. Most already have, and some, such as Spain, are still completing transposition.
It requires managing supply chain security: if you supply a regulated entity in Europe, you will be asked for evidence.
Key obligations
Management approves the measures, oversees their implementation and is accountable for them.
Policies, incident handling, continuity, encryption, access control and multi-factor authentication.
Security assessment of suppliers and service providers.
Early warning within 24 hours, notification within 72 hours and a final report within one month.
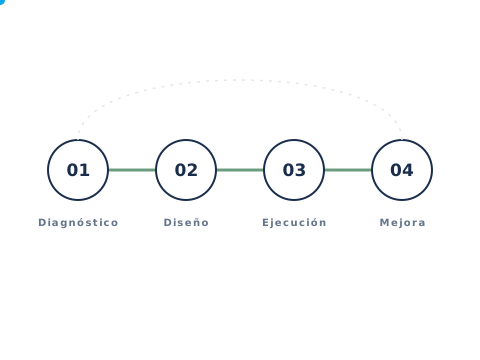
Phases
Entity types
Generally large companies in highly critical sectors such as energy, transport, banking, health, water or digital infrastructure. Proactive supervision.
Medium and large companies in other critical sectors such as postal services, waste, chemicals, food, manufacturing or digital providers. Reactive supervision.
Why NIS2
You reduce the impact of incidents that stop the business.
You meet the demands of your regulated clients in Europe.
The board understands and governs cyber risk.
We integrate NIS2 with ISO 27001, ISO 22301 and IEC 62443.
Who it applies to
FAQ
It is Directive (EU) 2022/2555, which sets a common level of cybersecurity across the European Union for essential and important entities in 18 critical sectors.
It can apply if you provide services in the EU in the covered sectors. In addition, your regulated European clients will require security measures from you as a supplier.
An early warning within 24 hours of detecting a significant incident, a notification within 72 hours and a final report within one month.
Up to 10 million euros or 2% of worldwide turnover for essential entities, and up to 7 million or 1.4% for important ones. Management can also be held liable.
In an initial assessment we tell you whether it applies, what type of entity you are and where to start.